The server sets a cookie with a Set-Cookie response header, and the browser then returns every matching cookie in one Cookie request header, name=value; name=value. Attributes such as expires, path and secure instruct the browser and never come back, so PHP sees only names and values in $_COOKIE, from the next request on. A cookie lives at most 400 days and holds a few kilobytes, so it should carry an ID, not the data:
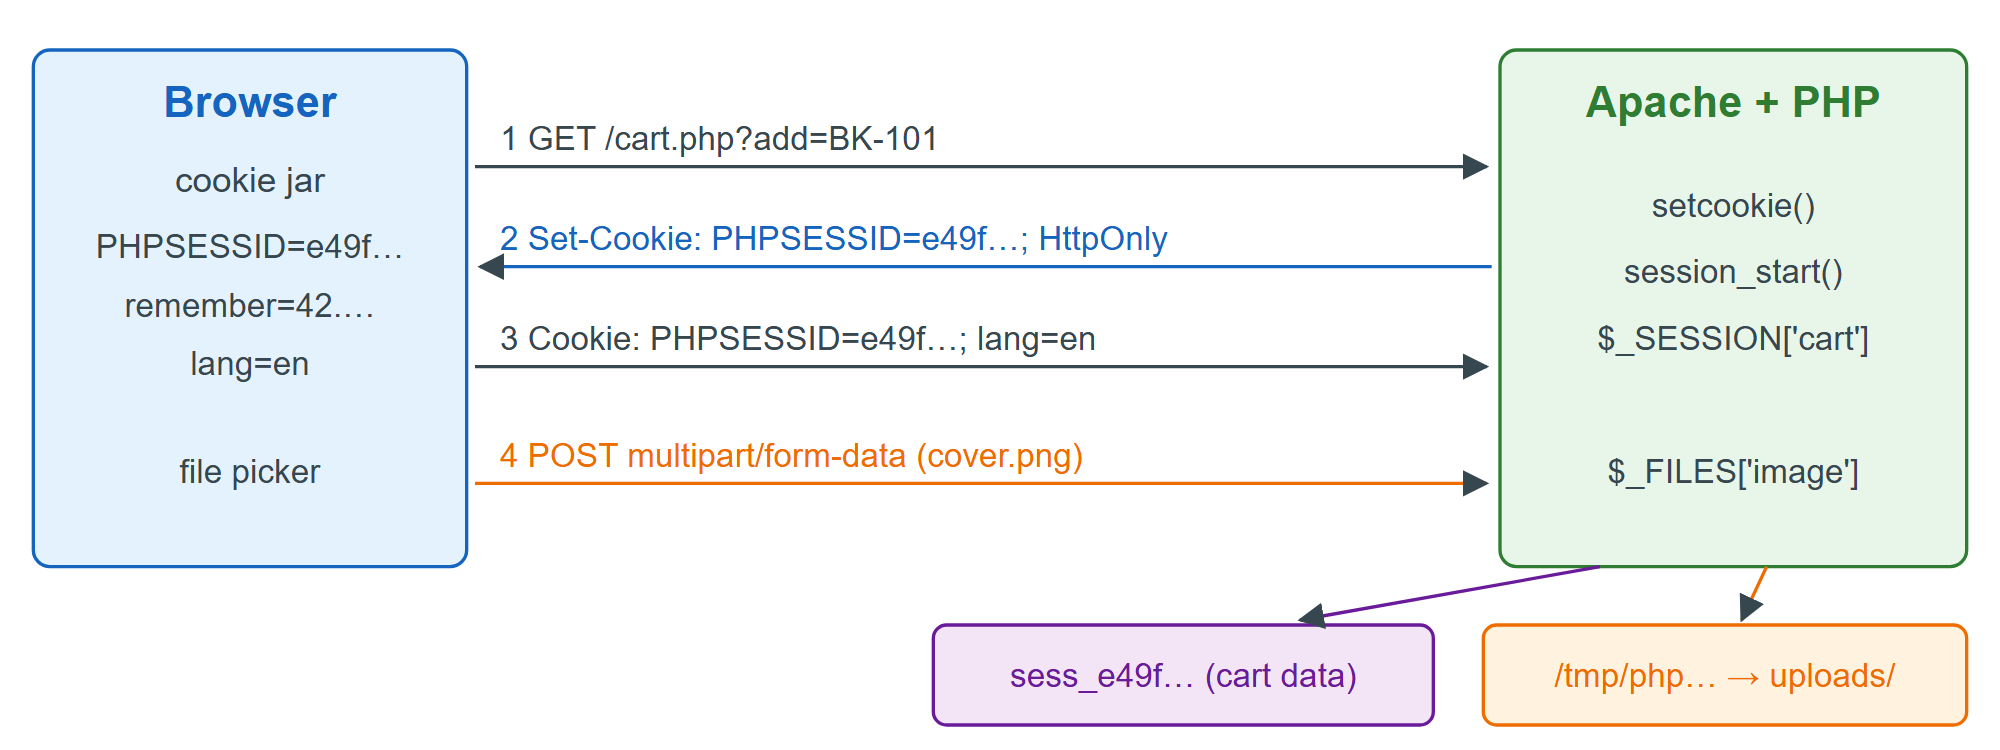
setcookie() and session_start() emit headers, so both must run before the first byte of output, even a space before <?php (Headers and Redirects).