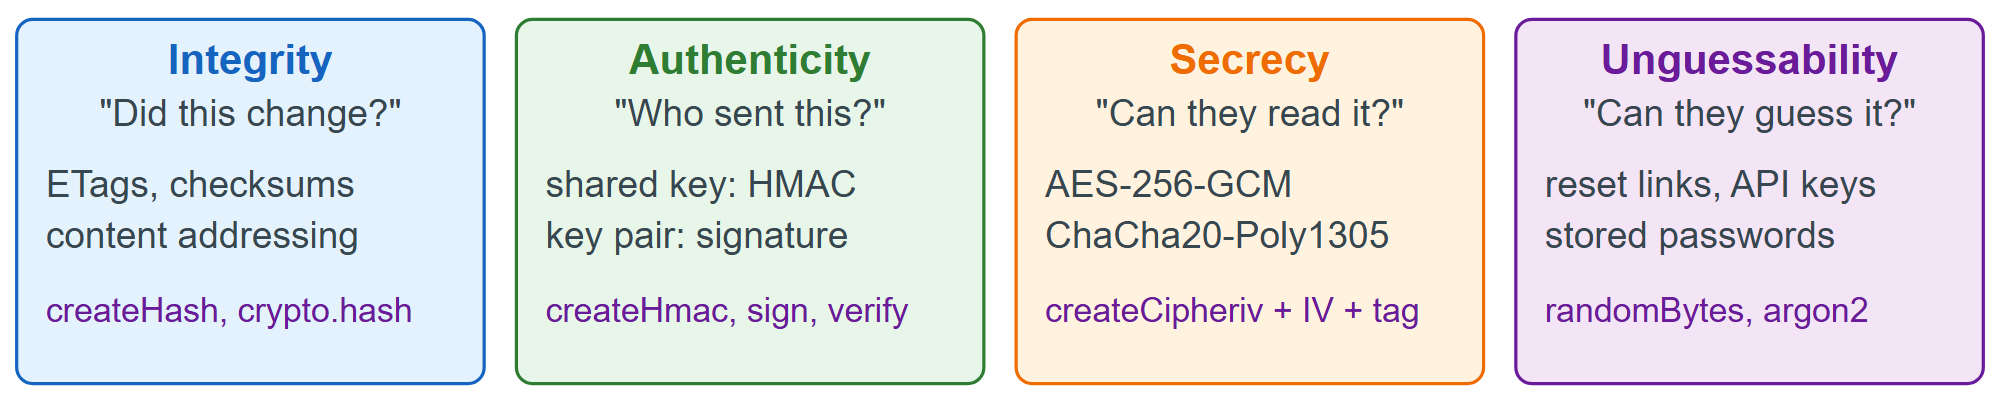
Every MERN application signs something: a tamper-proof session cookie, an unguessable reset link, a webhook provably from Stripe 238 . Node covers all of it in node:crypto, a binding over the OpenSSL library compiled into the runtime — process.versions.openssl is 3.5.5 on the Node 25.8.0 build used below. Two APIs ship in the box: the original callback- and stream-shaped one, and the Web Crypto API on crypto.subtle, promise-based and identical to what browsers and Cloudflare Workers 2 expose (The Web Crypto API in Node). Prefer Web Crypto for portable code, the Node API for scrypt, X.509 parsing and streaming.
One rule outranks that choice: use a primitive, do not invent a protocol. Almost every authentication break in the wild is a correct primitive used wrongly — a nonce reused, a MAC compared with ===, a token accepted without checking its algorithm — so each subsection below shows the failure as well as the success.