A MERN application is mostly other people's code. A modest Express 24,430 and Mongoose 243,355 server resolves to a few hundred packages, and every one runs with your process's full privileges: it can read .env, open sockets, spawn cmd.exe. The cheapest path into your production database is often a maintainer's compromised npm 2,036 account three levels down the tree, not your code.
The defenses split in two: the supply chain is what reaches disk before the program starts, and runtime hardening is what it may do afterward. Neither covers for the other.
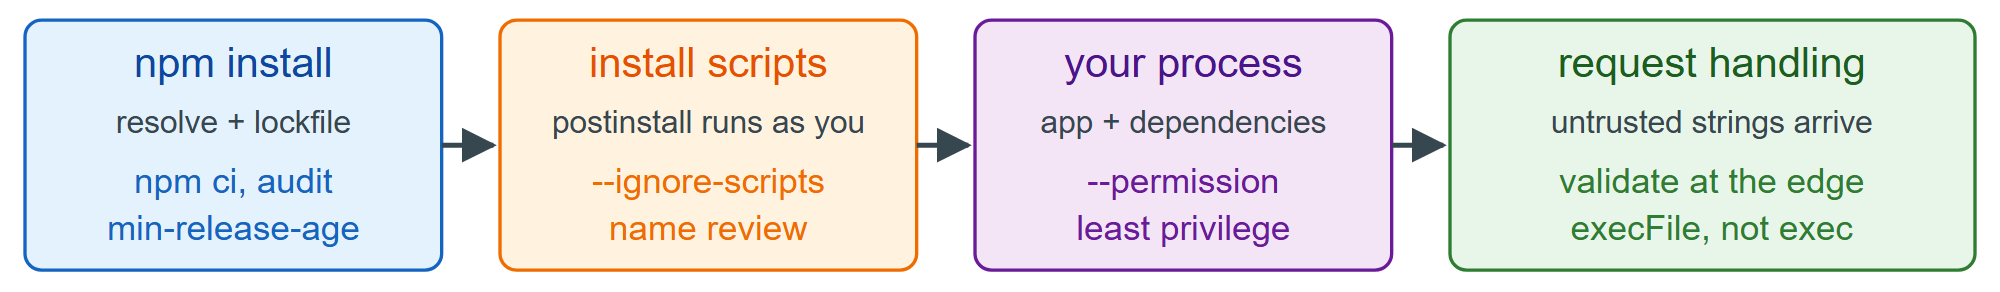
Output below was captured on Windows with Node.js 25.8.0 2,131 and npm 11.11.0; Node.js 26 differences are noted. Trusted Publishing covered provenance from the publisher's side; this is the consumer's.