A guard decides how a request proves who it is: the default web guard is a SessionGuard that trusts the session cookie. A provider decides how the user is loaded: users queries App\Models\User through Eloquent. The model implements the Authenticatable contract, so the guard can ask any user for its id, password hash and remember token.
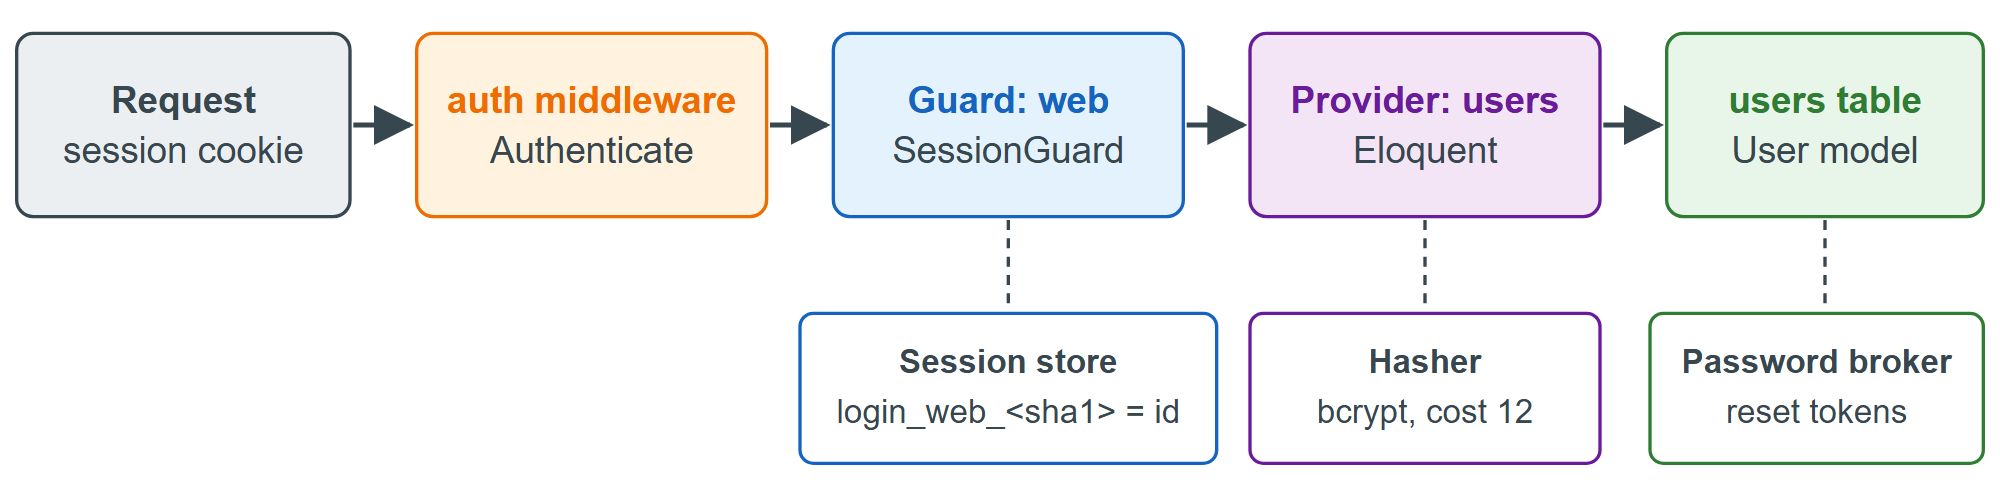
The session holds only the id, under login_web_59ba36addc2b2f94... (guard name plus the SHA-1 of its class), so each request costs one query to reload the user. Middleware applies it all: auth redirects guests to the route named login (JSON clients get 401), guest keeps signed-in users off the login page, verified demands a confirmed email, and password.confirm asks for the password again. Fortify 1,761 and the kits add nothing beneath this layer.