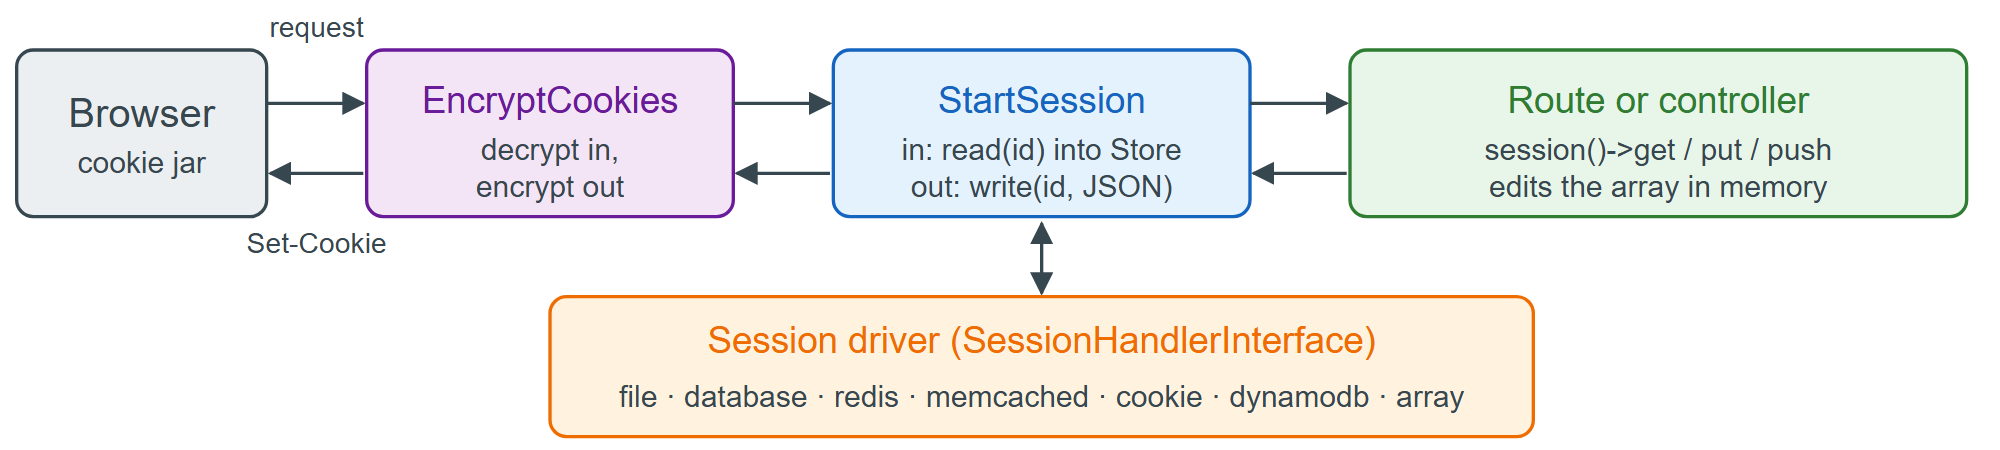
A Laravel 2,157 session is an array held by an Illuminate\Session\Store. The StartSession middleware of the web group (Global and Group Middleware) reads the 40-character ID from the laravel-session cookie, loads the payload through the configured driver, and after the route returns writes the array back and sets the cookie. $_SESSION stays empty. A /cart/add/{sku} route calls $request->session()->push('cart.items', $sku) and increment('cart.count') and returns the cart:
curl -si -c jar $B/cart/add/BK-PHP-01 | grep -E '^(HTTP|Set-Cookie|\{)' \
| sed -E 's/(=eyJ[^;]{6})[^;]*/\1.../; s/ expires=[^;]*;//'HTTP/1.1 200 OK
Set-Cookie: XSRF-TOKEN=eyJpdiI6I...; Max-Age=7200; path=/; samesite=lax
Set-Cookie: laravel-session=eyJpdiI6I...; Max-Age=7200; path=/; httponly; samesite=lax
{"cart":{"items":["BK-PHP-01"],"count":1}}Both values are encrypted (Cookies). Max-Age=7200 is SESSION_LIFETIME=120 minutes, an idle timeout that each request renews; XSRF-TOKEN omits httponly for JavaScript (CSRF Protection).
The Laravel 13 skeleton sets 'serialization' => 'json' in config/session.php, so only arrays and scalars survive; 'php' keeps objects but invites a gadget-chain attack if APP_KEY leaks.