Lakekeeper (https://github.com/lakekeeper/lakekeeper 1,473 ) (Apache-2.0, 0.13.6 on 22 September 2026, maintained by Vakamo, which sells a Plus edition) implements the REST specification in Rust on its own fork of the iceberg-rust crates: one 167 MB binary with "no JVM or Python env required", plus PostgreSQL 15 1,289 or newer. It adds OpenID Connect login, OpenFGA authorization, credential vending and signing, change events and a web console. demos/ch08/catalogs/run_lakekeeper.sh starts a PostgreSQL 18 container, runs lakekeeper migrate, serves on port 31182 and bootstraps the server. A warehouse then binds a name to a storage profile and the credential Lakekeeper itself uses; Spark 129 needs only the URI and the warehouse name (copy_to.py copies the tables):
# Register a warehouse in Lakekeeper, copy BookNest's order tables into it, ask for one back.
LK=localhost:31182
curl -s -X POST $LK/management/v1/warehouse -H 'Content-Type: application/json' \
  -d @"$DEMOS/catalogs/lk_warehouse.json" | jq -c '{name, "storage-profile": ."storage-profile"
  | {flavor, "remote-signing-enabled", "sts-enabled"}}'
bash "$DEMOS/scripts/spark.sh" catalogs copy_to.py lk orders,order_items \
  uri=http://$LK/catalog warehouse=booknest
P=$(curl -s "$LK/catalog/v1/config?warehouse=booknest" | jq -r .defaults.prefix)
curl -s $LK/catalog/v1/$P/namespaces/booknest/tables/orders | jq -r '.config | to_entries[]
| select(.key | test("^s3\\.(remote|signer.uri|endpoint)")) | "\(.key) = \(.value)"'{"name":"booknest","storage-profile":{"flavor":"s3-compat","remote-signing-enabled":true,"sts-e
nabled":false}}
+------+------+----------+
|orders| lines| gross|
+------+------+----------+
|100000|137944|3303427.30|
+------+------+----------+
s3.signer.uri = http://localhost:31182/catalog/
s3.endpoint = http://localhost:31900/
s3.remote-signing-enabled = trueThe copies reproduce the 3,303,427.30 baseline although catalog lk had no S3 keys: the table's config told Spark to send each S3 request to Lakekeeper for signing, so only Lakekeeper holds MinIO 30,943 's credentials and can refuse what it does not authorize (sts-enabled: true would vend temporary credentials instead). The console at /ui browses the result:
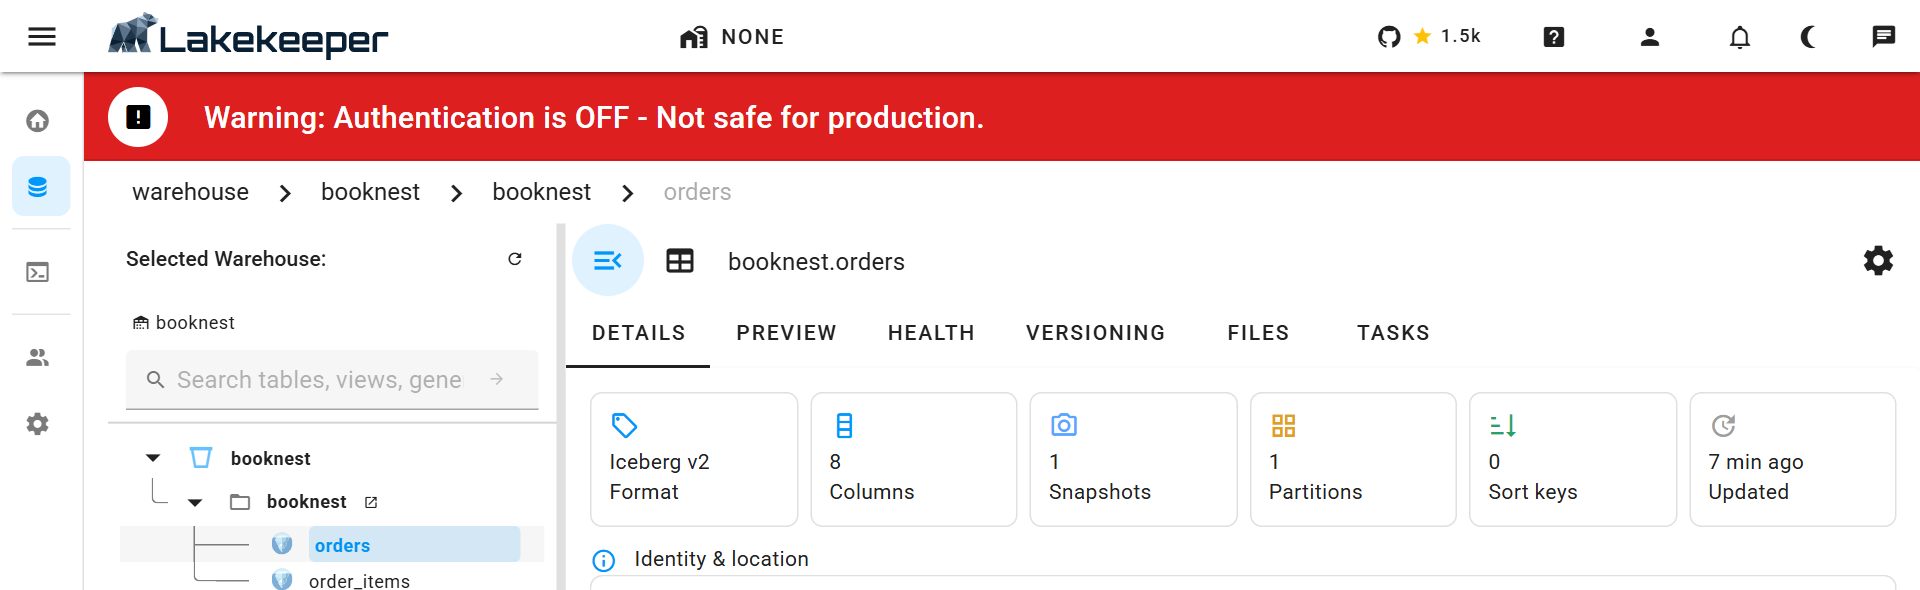
Authentication is off here, as the banner says; configure OpenID Connect and OpenFGA before bootstrapping. Resident memory was 83 MiB (plus 98 MiB for PostgreSQL), against 411 MiB for Nessie and 238 MiB for the fixture.