A root daemon means whoever controls it controls the host (Daemon and Socket). Rootless mode runs dockerd, containerd 234,762 and every container as an ordinary user inside a user namespace (User Namespaces): container root maps to your UID, other UIDs to your /etc/subuid range, and an escape lands in an unprivileged account.
Three helpers make that work. RootlessKit 1,304 (github.com/rootless-containers/rootlesskit (https://github.com/rootless-containers/rootlesskit 1,304 )) creates the user, mount and network namespaces and runs the daemon inside them, using the setuid newuidmap and newgidmap helpers from the uidmap package to install the subordinate ID ranges. Because an unprivileged user may not create real network interfaces on the host, container traffic leaves through a user-mode network stack: pasta (from the passt project, passt.top (https://passt.top/ 196,146 )) or the older slirp4netns. The daemon runs as a systemd 142,543 user service and listens on $XDG_RUNTIME_DIR/docker.sock instead of /var/run/docker.sock.
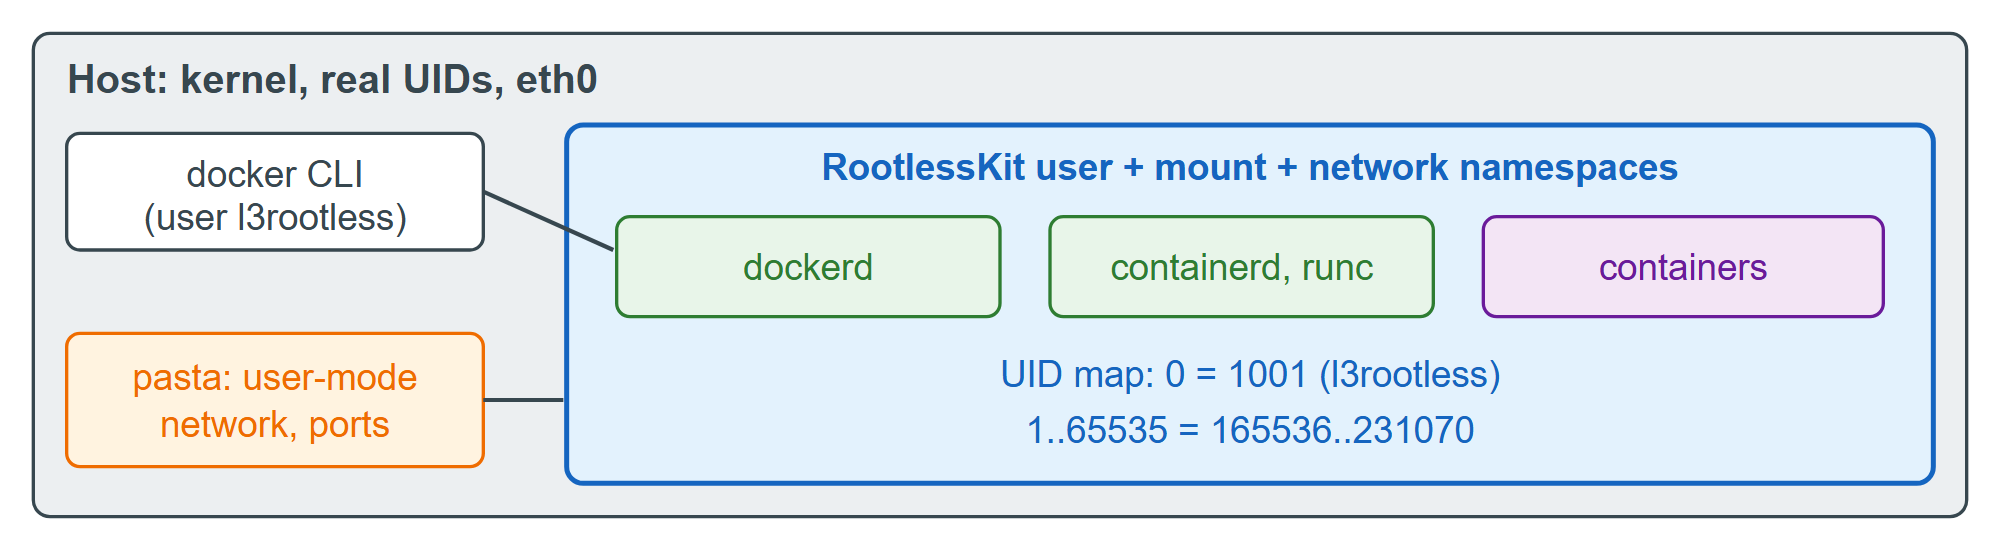
Unlike userns-remap, which remaps containers but keeps a root daemon, rootless mode removes root entirely. Podman 47,580 (Docker and Its Alternatives) is rootless by default on the same building blocks.