A vulnerability reported in a public issue is disclosed before it is fixed. SECURITY.md (in the root, docs/ or .github/) tells finders where to go instead; pull request #27 added one. Private vulnerability reporting adds a Report a vulnerability button that opens a private advisory only maintainers see:
gh api -X PUT repos/{owner}/{repo}/private-vulnerability-reporting
gh api repos/{owner}/{repo}/private-vulnerability-reporting{"enabled":true}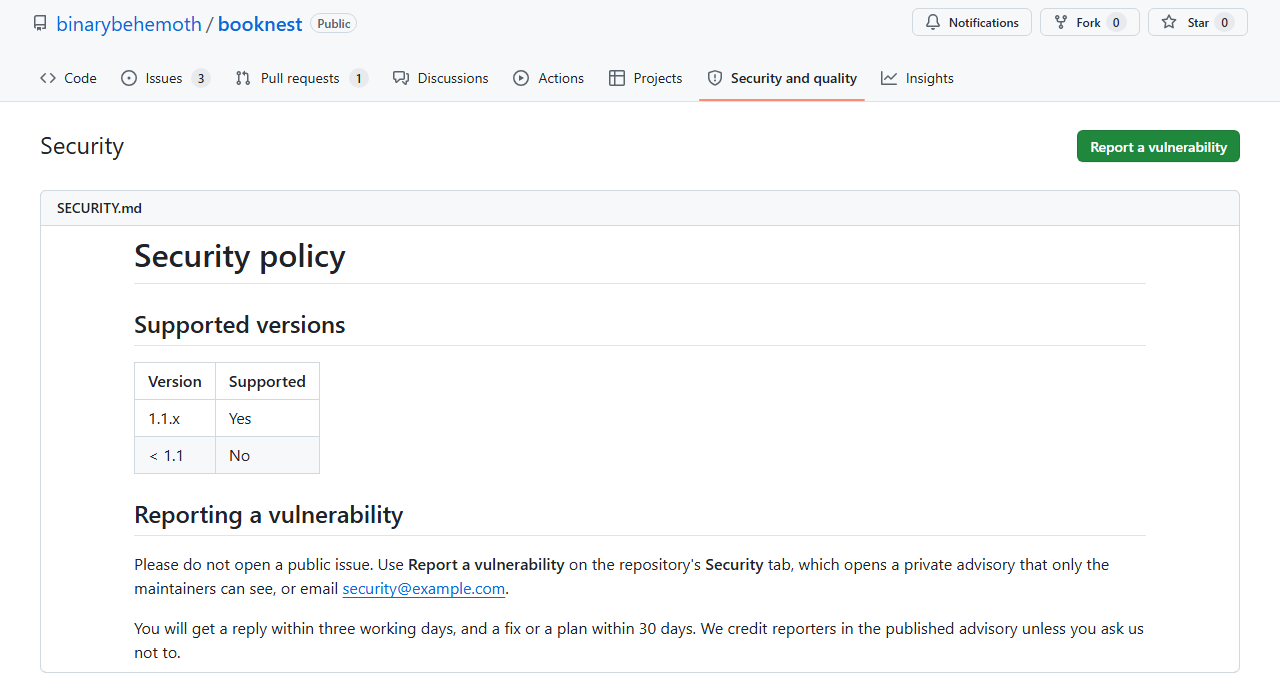
A repository security advisory is the maintainers' side. Creating one needs the Repository security advisories permission this token lacks (403), so it is not run here. A draft records the affected package, vulnerable and patched versions, CVSS severity and CWE; a temporary private fork lets invited collaborators fix it unseen, and GitHub 29 , a CVE Numbering Authority, can assign a CVE ID. Once published and reviewed, it joins the GitHub Advisory Database, and Dependabot 29 alerts every repository using the vulnerable versions (Dependabot).