The Groovy Sandbox met the sandbox from the inside; administrators meet it through In-process Script Approval, where refused signatures queue. A typical request is a Pipeline that wants to look at another job, here sec-sandbox:
def main = Jenkins.get().getItemByFullName('booknest/main')
echo "main's last build: ${main.lastBuild.number}"
Build 3 was refused. An administrator approved that one signature, and build 4 was refused one call later:
Scripts not permitted to use staticMethod jenkins.model.Jenkins get. Administrators can decide
  ...
...
Scripts not permitted to use method jenkins.model.Jenkins getItemByFullName java.lang.String.
  ...
Approvals creep this way: a team that clicks Approve until the build is green hands every Pipeline on the controller the whole Jenkins 8,793 API. Neither was flagged; only signatures on Script Security's list of dangerous ones, such as the new java.io.File left from The Groovy Sandbox, get the red warning:
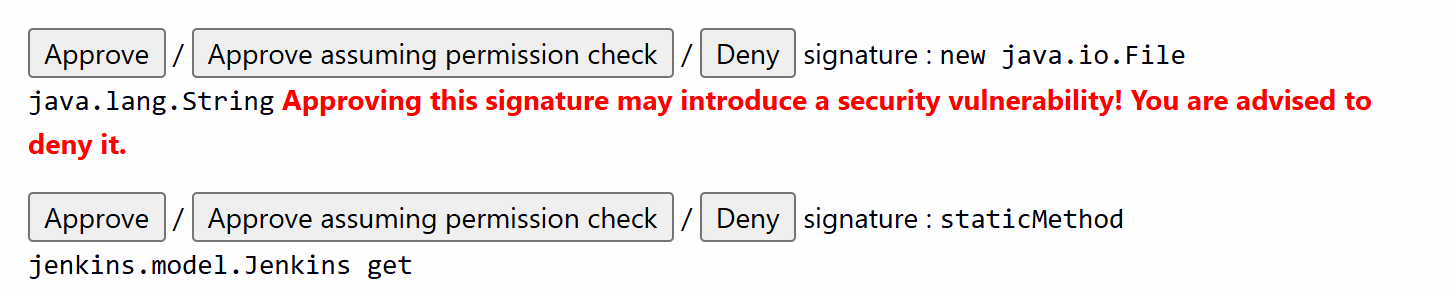
Both were denied and the approval revoked. Put such code in a trusted global library (Shared Libraries), which runs outside the sandbox but changes only through review. "Force the use of the sandbox globally" on the Security page goes further: every script runs sandboxed, and no new requests reach the approval page.