The Jenkins 8,793 security team publishes advisories at jenkins.io/security/advisories (https://www.jenkins.io/security/advisories/ 8,793 ) (with an RSS feed), usually on a Wednesday, together with the fixed releases. The advisory of 2 September 2026 is typical: 13 core issues, fixed in weekly 2.580 and LTS 2.568.3, among them a deserialization flaw, a session fixation and a leak of the CSRF crumb of CSRF Protection to other origins, plus fixes for 17 plugins such as Script Security, LDAP and Pipeline: Groovy Libraries. The File Parameter plugin's path traversal allowed remote code execution, and the Parameterized Remote Trigger plugin had no fix at all: the advice for such plugins is to remove them.
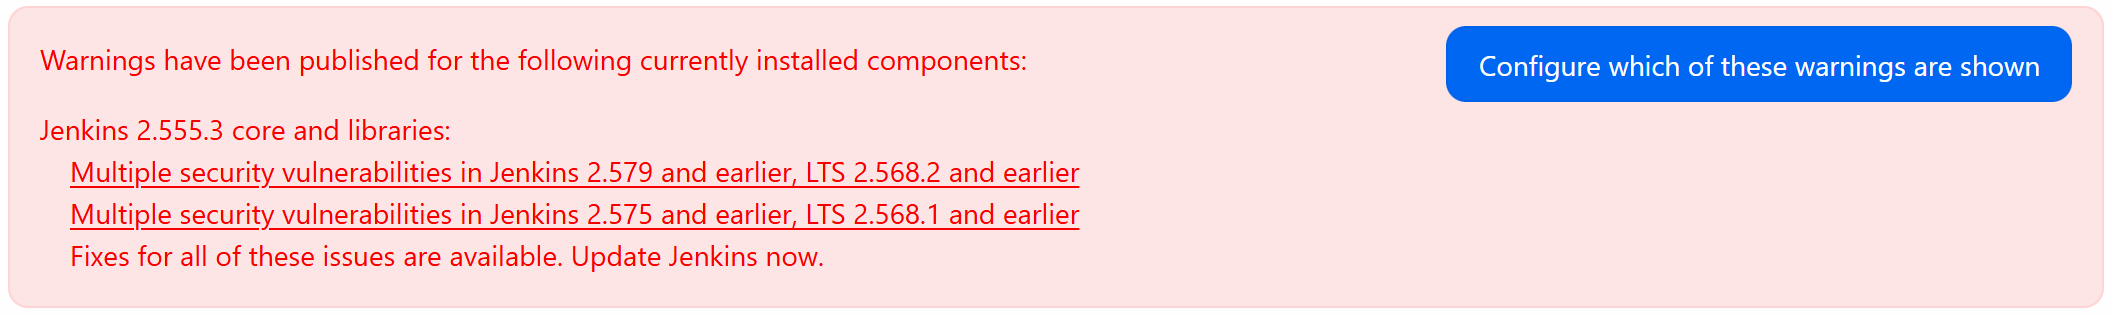
Controllers read the same data from the update center. l2-jenkins, on 2.568.3 with current plugins, showed nothing, but the 2.555.3 controller of LTS Upgrades displayed this on Manage Jenkins:
A routine that works: run LTS; read each advisory the day it appears; update plugins through plugins.txt and a rebuilt image (Bootstrapping a Controller), smoke-tested on a copy of the controller; and keep the plugin list short (Retiring Plugins), since every plugin you drop is one fewer advisory to act on.